Dutch Arrest in ShinyHunters Case Raises Corporate Cybersecurity Questions
The detention of a 24-year-old Amsterdam cybersecurity worker puts executive hiring, risk controls, and incident governance under renewed scrutiny.
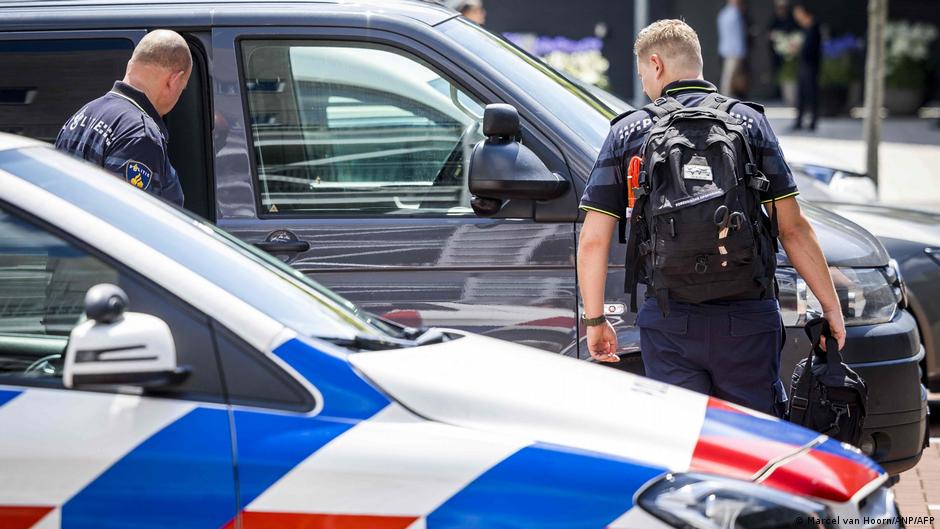
Dutch police have detained a 24-year-old Amsterdam resident as part of an investigation into ShinyHunters, the hacking group that last week claimed it had breached a database connected to FBI agents. The case is drawing attention far beyond law enforcement because the detained man is believed to be an information technology professional with a prior conviction for data theft and extortion.
Police in the Netherlands announced on Monday, September 28, that they had arrested a 24-year-old man from Amsterdam in connection with an investigation into the activities of ShinyHunters. The group said last week that it had breached a database of the U.S. Federal Bureau of Investigation and stolen data belonging to agency employees.
The police statement on X did not give the exact date of the arrest, saying only that it took place in September. The suspect is due to appear in court in Rotterdam on Tuesday, September 29. Police also did not disclose his name.
Benjamin Corper, a representative of Amsterdam-based cybersecurity company Neo Security, told Reuters that the detained man is Pepijn van der Stap, who leads the company’s offensive cybersecurity practice. According to Corper, his employee was detained on September 15 “during a large-scale police operation using flash-bang grenades.” On the same day, forensic officers visited Neo Security’s office.
ShinyHunters said van der Stap “has nothing to do” with the group.
A Second-Chance Hire Becomes a Boardroom Risk
For corporate leaders, the case lands at the intersection of cybersecurity staffing, reputational risk, and executive oversight. Offensive security teams often employ specialists who understand intrusion techniques, vulnerability discovery, and adversarial methods. But when such roles are filled by individuals with criminal histories involving data theft, boards and executives face a difficult governance question: how to balance redemption and scarce technical talent against operational and reputational exposure.
Van der Stap was sentenced in 2023 to four years in prison, one year of which was suspended, after a court found him guilty of a series of data thefts and extortion. Law enforcement authorities estimated that he earned between 1.5 million and 2.7 million euros from those crimes.
According to the investigation, van der Stap committed the offenses while working at Hadrian, an Amsterdam cybersecurity startup, and while volunteering with DIVD, a nonprofit research organization focused on identifying computer vulnerabilities. During the trial, he admitted guilt and expressed remorse.
He was released early in December 2025. In an interview with Brian Krebs, author of the KrebsonSecurity blog, shortly before the new arrest, van der Stap described himself as a hacker who had taken the path of reform, was trying to change his life for the better, and wanted to benefit society. Corper described his employment at Neo Security as a “second chance” for his employee.
That framing may now carry consequences for Neo Security’s leadership. Even without a finding of guilt in the current matter, the arrest could force the company to explain its hiring process, internal controls, client safeguards, and the degree of access granted to senior offensive security personnel. For clients, especially those buying penetration testing or red-team services, the case may sharpen due diligence questions around background checks, supervision, segregation of duties, and contractual data protections.
Alleged FBI Data Theft Broadens the Stakes
On September 22, ShinyHunters published a message on the dark web claiming it had breached an FBI database and stolen data on many former and current bureau employees. The group said the data included information on psychiatric and medical examinations of agents. It also claimed to have obtained access to data belonging to FBI Director Kash Patel. Reuters was able to partially verify the authenticity of the published data.
FBI representatives said they were “aware of claims of unauthorized activity” affecting the FBIjobs.gov applicant website and were investigating. The bureau’s statement leaves open the central questions that matter to both public-sector agencies and private employers: what systems were accessed, what data was exposed, and whether the incident involved a direct compromise or a third-party pathway.
For American companies, the alleged FBI breach is a reminder that sensitive employee and applicant data can become a high-value target even when it is not part of a core revenue system. Medical, psychological, employment, and identity records can create legal exposure, reputational damage, and personal safety concerns. Those risks are especially acute for institutions that employ law enforcement, defense, intelligence, or critical infrastructure personnel.
The incident also underscores the challenge of crisis governance. Executives must move quickly to verify claims, preserve evidence, notify affected parties where required, and communicate with regulators and customers without overstating what is known. In that environment, vague attacker claims, partial data dumps, and third-party verification all become pressure points for the board and C-suite.
ShinyHunters has also been linked to several other major data leaks. In February 2026, after the databases of Odido, the largest mobile operator in the Netherlands, were breached, the group obtained access to data on more than 6.2 million residents of the country. Other recent attacks attributed to ShinyHunters include the alleged theft of millions of corporate records from video game developer Rockstar Games, known for the Grand Theft Auto series, and a May attack on the Canvas education platform that caused widespread disruptions in U.S. schools.
Taken together, the allegations point to a threat profile that has direct implications for corporate strategy. Data-rich organizations in telecom, gaming, education, government services, and cybersecurity are all facing adversaries that seek both scale and sensitivity. The Dutch arrest may ultimately prove to be one investigative step in a broader law enforcement effort. But for corporate boards, the lesson is already plain: insider access, security talent management, and breach readiness are no longer technical back-office issues. They are governance issues with enterprise-level consequences.